NowAIKit 5.1: from a zero-day headline to a closed incident
5.0 put real ServiceNow forms inside the chat. 5.1 is about the work security, platform and CMDB teams do every week: a named threat traced across Vulnerability Response and Security Incident Response, ACLs that deny as well as allow, dashboards on Platform Analytics, a CSDM-aware CMDB, and reports that show where every number came from.
npm i -g nowaikit@latest, then nowaikit doctor. Free for individuals, and it always runs with your own ServiceNow permissions.
Zero-day response, the way security teams actually run it
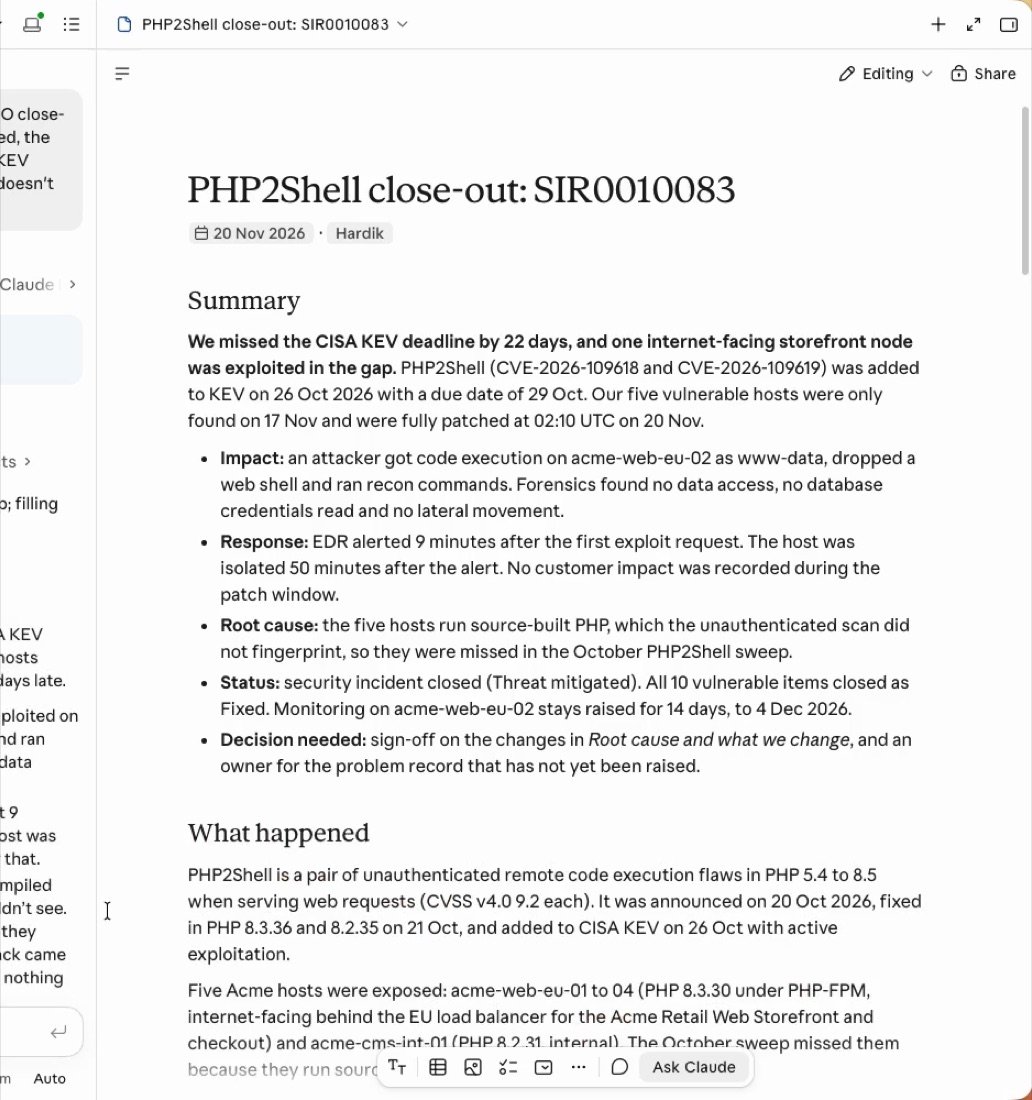
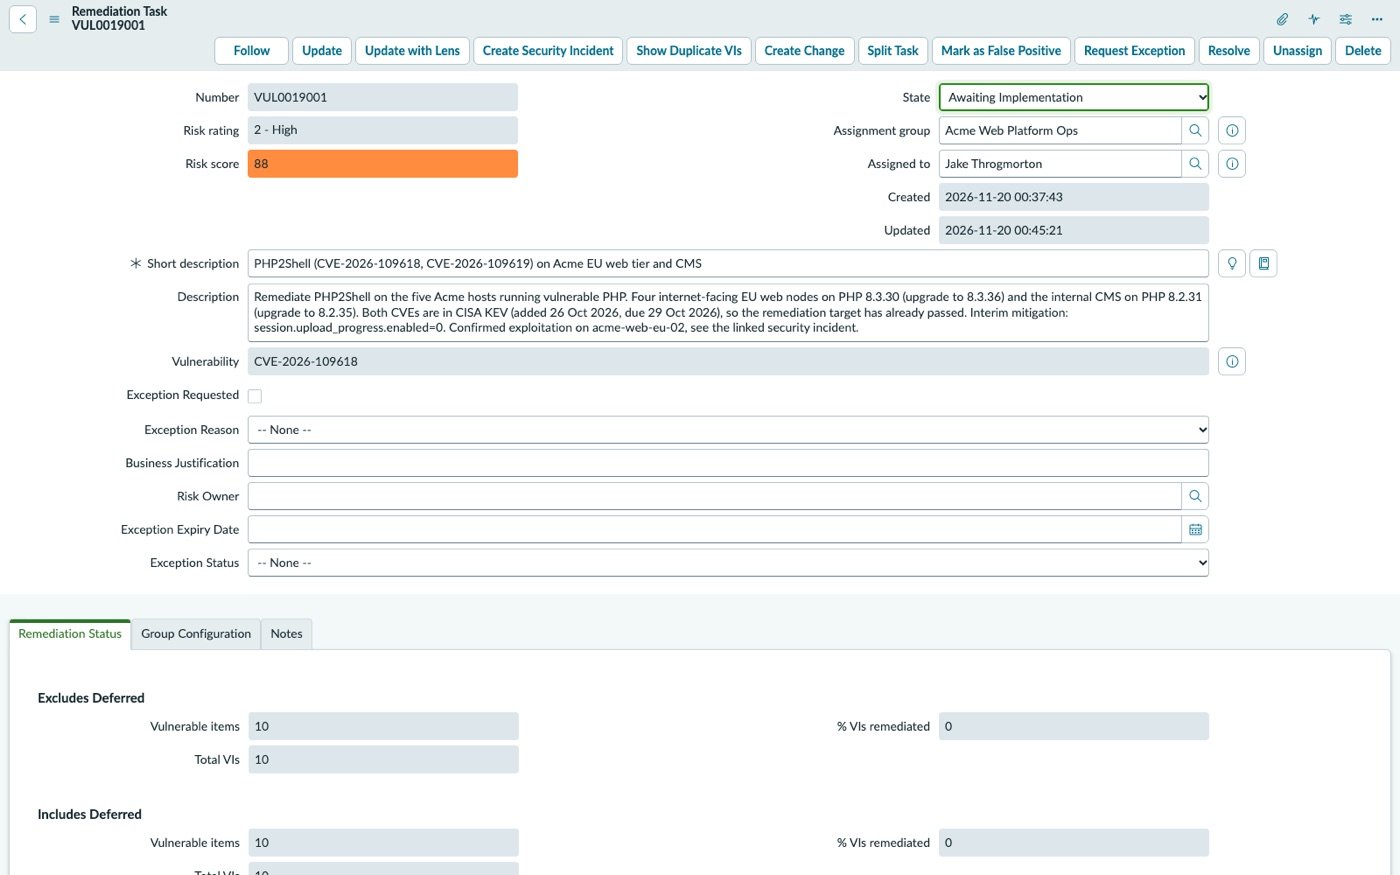
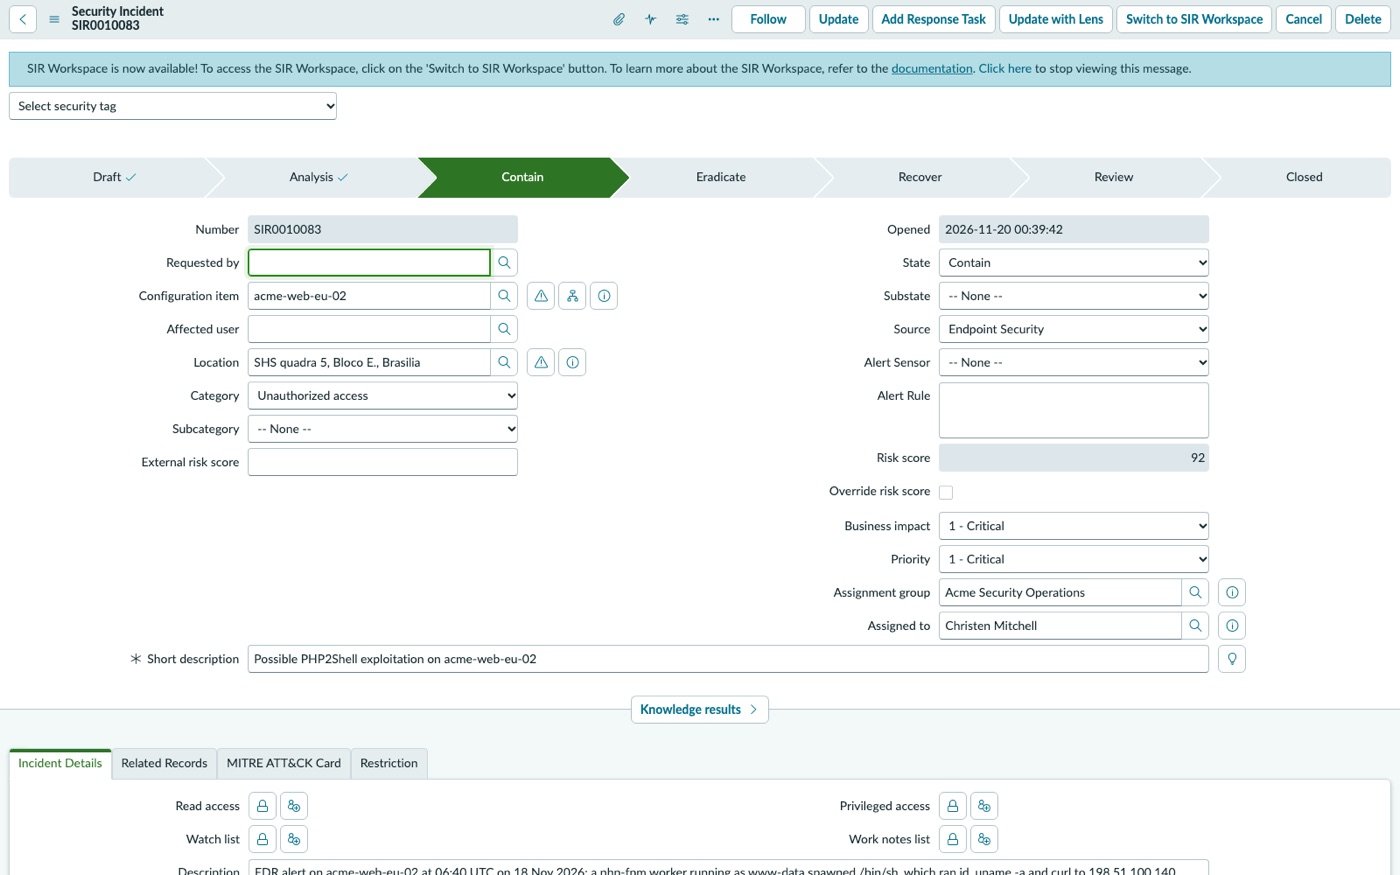
When a vulnerability like PHP2Shell lands on the CISA Known Exploited Vulnerabilities list, the questions come in a fixed order. Are we exposed? Which systems? How bad, and what's the deadline? Is the patch moving? Was anything already hit? We built 5.1 around that order and tested it end to end on a demo instance with the full storyline: two CVEs, ten vulnerable items on an internet-facing PHP web tier, a remediation task, an emergency change, a mitigation change and a security incident in Contain.
get_threat_statusfollows one named threat across CVE entries, vulnerable items, the business services behind them, remediation tasks, changes, exceptions and security incidents, in one call.get_kev_compliancechecks every KEV item against its CISA due date: fixed on time, fixed late, open and overdue, with days past due.create_change_from_remediation_taskraises the change through Vulnerability Response's own Create Change, so the change and its vulnerable items stay linked and their states keep moving together.- Vulnerable item and remediation task tools read the right tables on current releases, security incident states use their real labels, and CIs link through to the CMDB.
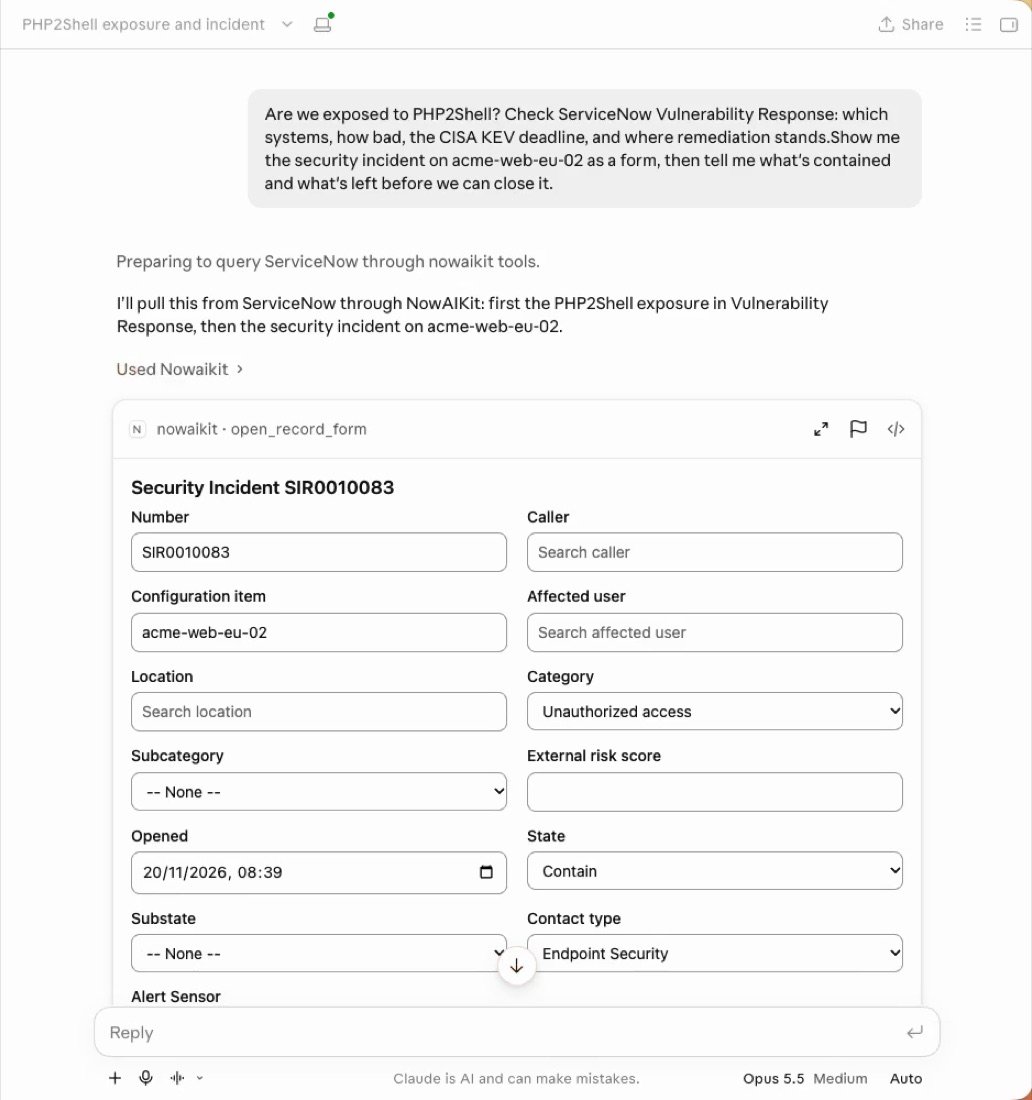
Three new Apex skills package the workflow: zero-day-response for the war-room view, kev-compliance-report for the CISA deadline audit, and vuln-exposure-brief for the one-page exposure summary leadership asks for.
Everything it reads is a normal ServiceNow record your team can open and check.
Built for Australia and Brazil
The last two ServiceNow releases changed things admins rely on. 5.1 keeps up so your AI client does too.
- Platform Analytics dashboards.
list_pa_dashboardsandget_pa_dashboardread the new Platform Analytics dashboards as well as the legacy Core UI ones, with tabs, widgets, permissions and workspace visibility.get_dashboard_migration_statusshows how far the move has got. - Deny Unless ACLs.
create_aclandupdate_acltake a decision type, conditions, security attributes and required roles, and they refuse roles that don't exist. From Brazil an ACL that names a missing role denies everyone, so this check matters.get_acl_posturecounts allow and deny ACLs and lists the ones with missing roles. - CSDM life cycle.
cmdb_reconcilecan retire CIs using install status, the CSDM life cycle stage or both, and the CMDB find tools return both field sets.get_csdm_healthandget_cmdb_data_foundationsshow where the CMDB stands. - Release awareness.
get_release_infonames the current and next release family and checks the known Australia and Brazil changes against your instance, with live counts.scan-upgradeuses it.
See inside your AI platform
More teams now run Otto skills and AI agents in production, and governance questions follow. 5.1 answers them from the instance.
get_ai_model_providersshows which model provider sits behind each Otto skill and agent capability.get_agent_access_matrixshows who can run each AI agent, andget_ai_runtime_metricsshows how they're being used.list_agent_teams,list_agent_strategies,list_external_agent_runsandlist_ai_inventory_cisfill in the rest, andlist_ai_agentsfilters by agent type, for example voice.get_mcp_exposurelists what your instance exposes over MCP, and themcp-exposure-reviewandai-governance-auditskills turn that into findings.
Answers to "what runs when?"
trace_table_operation lists everything that runs for one operation on one table, in order: business rules, flows, workflows, notifications, engines and more, with a Mermaid diagram you can paste into a design doc. Alongside it:
get_atf_code_coverageshows which scripts your ATF tests actually touch.list_process_mining_projectsandget_process_mining_findingsbring Process Mining results into the chat.get_integration_auth_posturefinds integrations still on Basic auth and other weak spots.
Reports you can check
Ten new Apex skills cover AI governance, CSDM data foundations, integration auth, MCP exposure, ATF coverage, table execution order, process insights and the three security skills above. Every report now works the same way:
- Grounded.
nowaikit runandnowaikit reportgather each skill's data with read-only calls before the model starts, link every record they cite, and list anything they couldn't gather instead of guessing. - Scored. A 0 to 100 score with area scores, stable finding IDs and an effort estimate per finding.
- Portable. PDF and PPTX, with a findings register in CSV and JSON next to each one for your tracker.
Pass arguments such as an incident or change number with --arg key=value.
Smaller things that help every day
nowaikit doctorwarns before a Basic auth connection breaks under ServiceNow's Basic auth restriction, accepts the CMDB rolessn_cmdb_adminandsn_cmdb_editor, and names your release.query_recordsnow says when a query names a field the table doesn't have. ServiceNow reports that as a permissions error, which used to send agents in the wrong direction.- Eight more Claude skills: change risk review, update set review, flow debugger, ACL auditor, AI governance, upgrade readiness, what runs when and ATF coverage.
Across the NowAIKit family
- NowAIKit Builder 1.3 for VS Code is out on the Visual Studio Marketplace and Open VSX.
- NowAIKit Utils 1.4, the browser extension, moves its AI assistant into Chrome's side panel, reads Workspace and Next Experience forms, adds a production guard and a rebuilt command palette, and can run Explain and Summarise on your own computer with Chrome's built-in model. It's in store review now.
Get it
npm i -g nowaikit@latest, then nowaikit doctor. Already set up? Your MCP client picks up 5.1 the next time it starts. Every 5.0 setting keeps working.
The full list is in the changelog, and the tools are in the tools reference.